

Necessary technologies like APIs, new and existing cloud environments, automation tools - can all become attack vectors and expose your organization to vulnerability.

What We Do Best
Our team of cloud cyber security experts is here to guide your organization through a smooth, secure cloud migration. We'll use cutting-edge tools like automation with Infrastructure as Code (IaC) and a unique Target Operating Model (TOM) to create secure Landing Zones and ensure rock-solid protection.
Whether it’s an existing cloud environment or applications intended for cloud deployment, we will assess your security posture, leveraging specialized SaaS products and cloud environment tools, including penetration tests. We’re here to tackle any vulnerability, and make sure your cyber protection is intact.
Our team studies your organizations’ various layers of protection - and plans, designs and implements tools to address each of them. From Endpoint Protection Platform (EPP), to applications (SecDevOps, CI/CD) through cloud environment and server protection, and lastly - the SIEM systems which monitor everything and provide the protective layer that oversees all security and cyber incidents.
We create solutions that are tailored to your organization, so we can achieve and maintain business resilience for the long run - for you.
The apps you develop and the websites that you use to provide services can become attack vectors - putting both your organization and your clients at risk and exposing you to lawsuits.
Strong foundations start with thorough penetration tests which give you a real idea of your organization’s vulnerabilities.
Our team specializes in conducting short, focused penetration tests - with a powerful business impact. The tests will include active and passive network security scans in order to detect whether there are any issues or vulnerabilities in one of your apps or websites, both on the cloud and on-premise.
The first step toward information security is cybersecurity governance. In order to create governance, organizations need to invest in locating and identifying risks, and create a strategy to address them. The combination between technological and strategic consulting provides our clients a full, clear picture of their security, privacy and regulation compliance standing.
Our experts come from a multitude of backgrounds - combining experience in methodology and policies, technology and a deep understanding of regulation and compliance.
Together, we help organizations like yours to gain understanding of their current status, define cybersecurity goals and create a strategic path of action to connect the dots.
Our team also guides organizations through compliance processes to gain certifications and accreditations, including:
- ISO27XXX
- GDPR
- Israeli Privacy Law
- HIPAA
- CMMC
Getting requests for SOC2 from clients? We’re here to guide you through the process.
The SOC2 (Service Organization Control) report was developed by the AICPA and defines the criteria for managing client data, based on trust principles criteria.
During the accreditation process, the organization is tested on its security, availability, confidentiality, privacy, and integrity of information.
The report is signed by KPMG as an independent accountant after an audit, according to the type of report.
Choose the right technological solutions for your organization, with our advanced platform, offering best-of-breed solutions.
When it comes to choosing cyber solutions, we believe only the best will do. Our disruptive approach to cyber technology selection streamlines your journey and generates better outcomes.
At KPMG Technology Consulting, we built a service environment that mimics yours so you can get a real idea of how each solution will work once you implement it in your organization.
Disruption can come from many directions, including cyberattacks, technology failures, and unexpected emergencies. The key question is how prepared your organization is to maintain critical operations when disruption occurs.
We help organizations assess how vulnerabilities and disruption scenarios could affect critical business processes through Business Impact Analysis (BIA). Based on these findings, we develop structured and tailored Business Continuity Plans (BCP) aligned with the organization’s operational needs.
Our team also plans and facilitates Disaster Recovery (DR) exercises to help validate that recovery plans work effectively in practice. Our approach extends beyond cybersecurity, providing organizations with a broader framework for maintaining operational and business continuity.
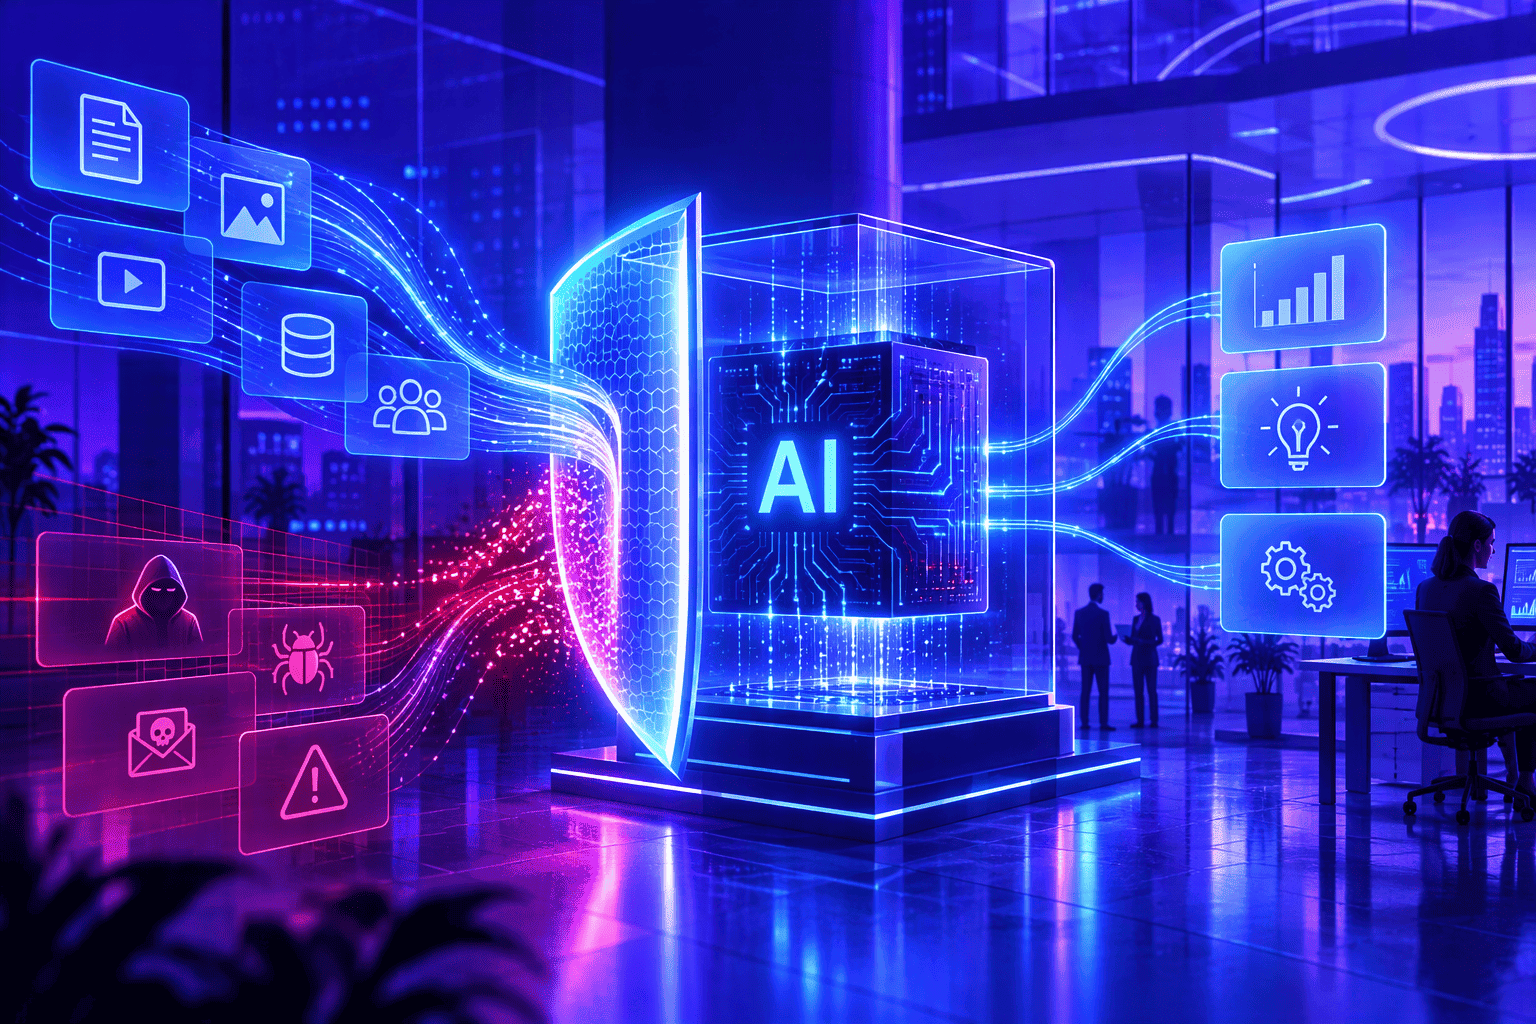
Artificial intelligence is transforming the way organizations operate. Alongside the business opportunities it creates, the growing use of AI also introduces new risks, including exposure of sensitive information, the use of unauthorized tools, and gaps in governance and oversight.
Our team helps organizations use AI services securely, from enterprise GenAI solutions to tools such as Copilot and Gemini. We help establish clear policies and guidelines for responsible AI use, identify risks relevant to your organization, and build a governance framework that enables you to realize the benefits of AI without compromising information security.
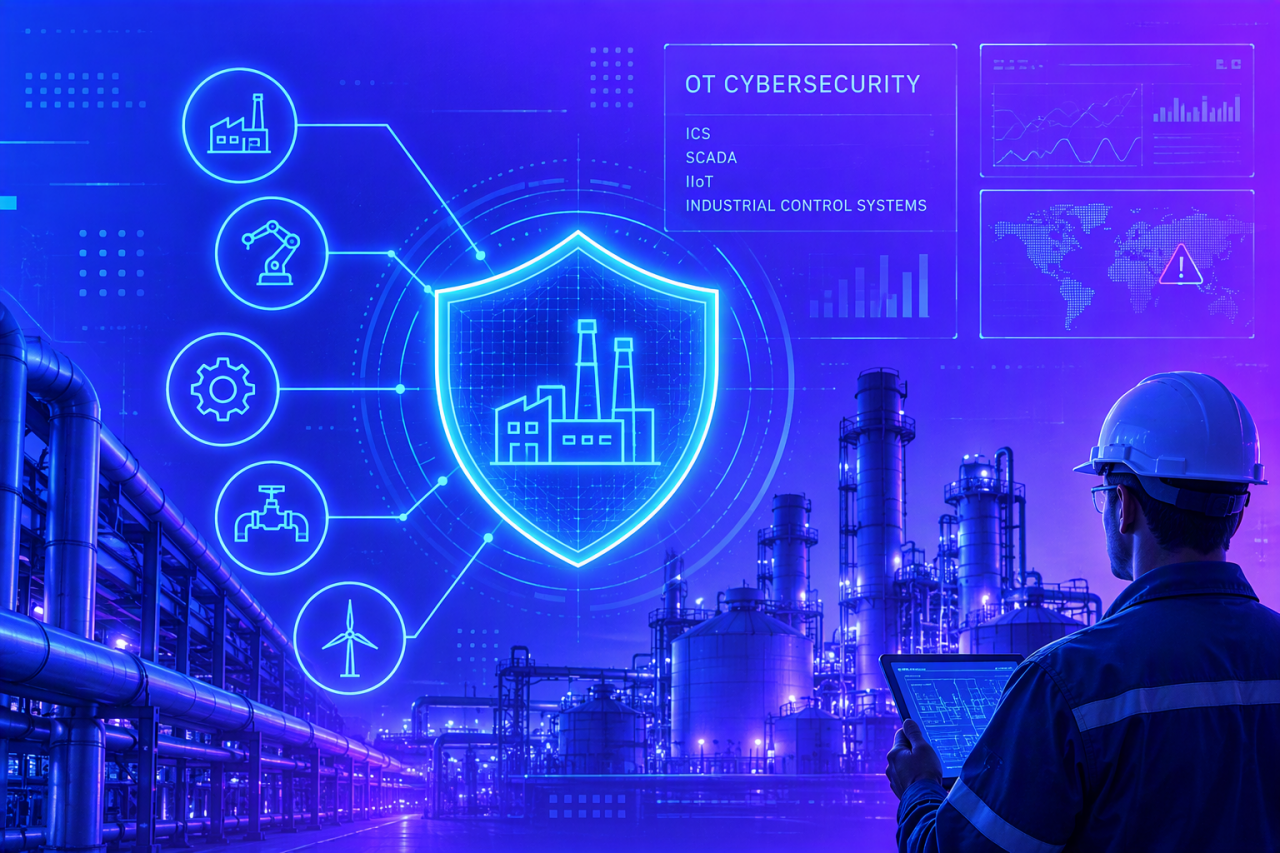
Operational and industrial systems are at the heart of many organizations. A cyberattack targeting these environments can disrupt production lines, affect critical services, and potentially compromise safety.
Our team specializes in strengthening cybersecurity across Operational Technology and Industrial Control Systems (OT/ICS/SCADA/IIoT). We understand the unique characteristics of these environments and the operational requirements that must be considered when protecting them.
We conduct regulatory and standards compliance assessments based on recognized OT/ICS cybersecurity practices and frameworks, including NIST SP 800-82 and IEC 62443. By identifying security gaps and recommending practical measures to address them, we help organizations strengthen the protection of their critical infrastructure and operational environments.
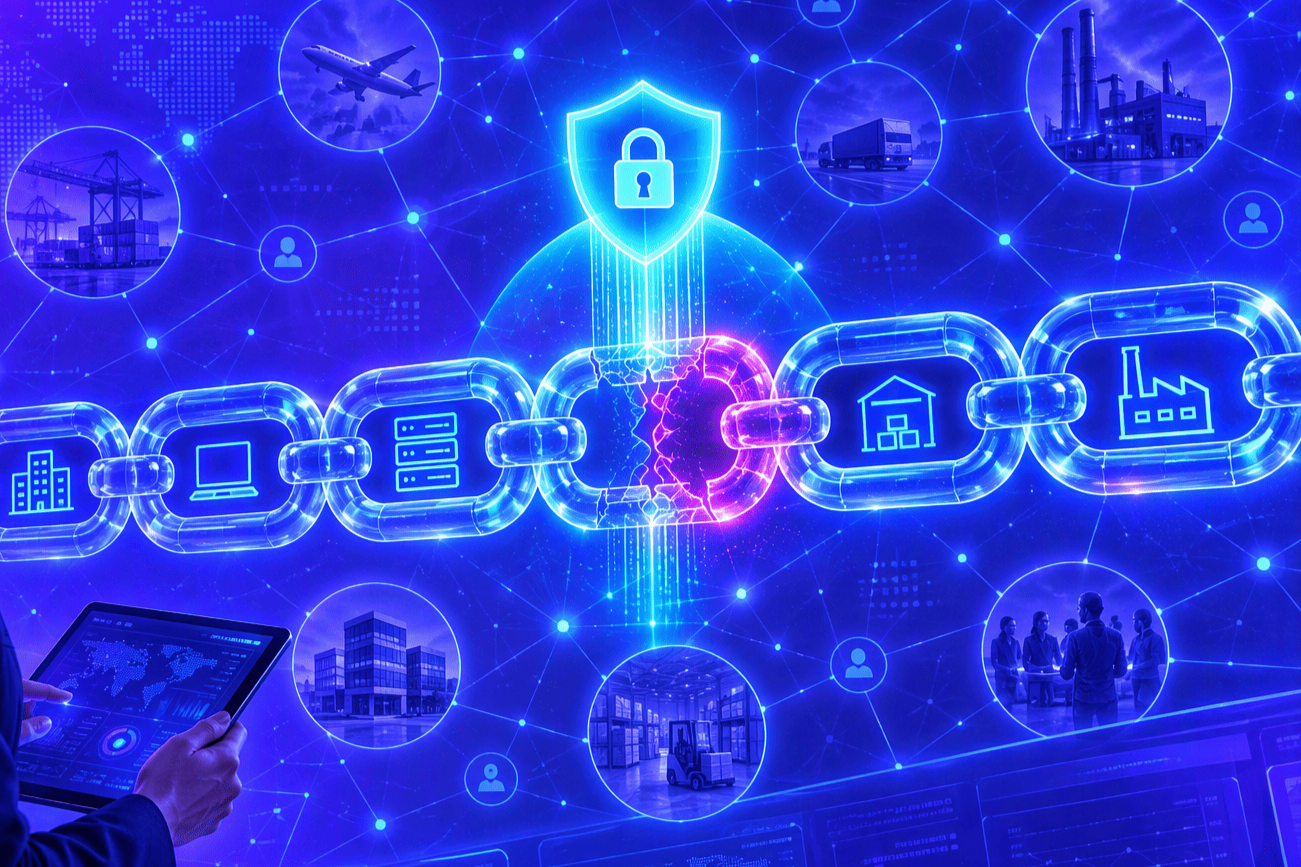
Your organization’s security is only as strong as the weakest link in its supply chain. Suppliers, service providers, and business partners with access to your systems and information can create indirect pathways for cyber threats.
Our team conducts information security assessments across the supply chain to identify vulnerabilities, evaluate third-party risks, and determine the measures required to reduce exposure.
We also support organizations in managing supplier information security and conduct on-site security assessments of suppliers. This provides greater visibility into third-party risks and helps organizations work with their business partners with greater confidence.
Why KPMG Technology Consulting?
Our team of advanced tech professionals offers groundbreaking technological solutions adapted to fit the unique needs of your business.
We come equipped with hard-earned experience and proven success across a range of high-profile projects.
We combine deep sector know-how with global understanding to transform your business vision into reality.
KPMG Technology Consulting
We bring value in key tech domains that are essential to any business

Overcome cybersecurity challenges to protect the future of your business
Lead your business to the cloud with confidence
From square one to a top-tier product
Harness data and ML to enable new business opportunities
Realize the full potential of SAP
Turn quantum readiness into resilience, innovation and business value.

Get in touch
Discover why organizations across Israel trust KPMG to make a difference and how we can help you do the same.