
      Risky Business

      This article is featured in our latest edition of Risky Business Magazine, dedicated to NIS2.

      In this issue:

      Want the full story? Read the complete magazine for additional perspectives, insights, and practical recommendations on today's cybersecurity challenges.


      Feeling overwhelmed by NIS2 and the new cybersecurity expectations it brings? You're not alone. As the EU’s updated cybersecurity directive, NIS2 significantly raises the bar for essential and important entities: introducing stricter requirements around governance, risk management, incident response, supply chain security, and certification. For many organizations, understanding where to begin can feel daunting.

      KPMG helps organizations navigate NIS2 by assessing their current maturity, identifying gaps, building actionable roadmaps, drafting or updating policies and procedures, and supporting implementation efforts. Whether your organization needs a maturity assessment, guidance on cyber fundamentals, or help implementing controls across IT and OT environments, our experts are here to support you.

      In this edition, the experts explain what NIS2 entails, how Cyber Fundamentals (CyFun) and ISO 27001 can be used to demonstrate compliance, and how KPMG supports organizations through workshops, roadmap development, policy writing, and certification guidance. They also share lessons learned from real client engagements, as well as their personal experiences of growing within KPMG.
      What is NIS2 and why is it important?

      Safae: NIS2 is an EU cybersecurity directive. Its main goal is to strengthen cybersecurity and resilience across both essential and important organizations. And in Belgium, two acronyms are important: the CCB, the Centre for Cybersecurity Belgium, and CyFun, the Cyber Security Fundamentals framework they published.

      CyFun is what guides companies in Belgium toward NIS2 compliance. It’s structured across six pillars - Govern, Identify, Protect, Detect, Respond, Recover - broken down into 22 domains. Those domains help companies understand what they must do to be compliant. Organizations can choose between Cyber Fundamentals or ISO 27001, depending on their existing maturity and structure.

      Also important to mention is that essential entities must be certified by April 2027.

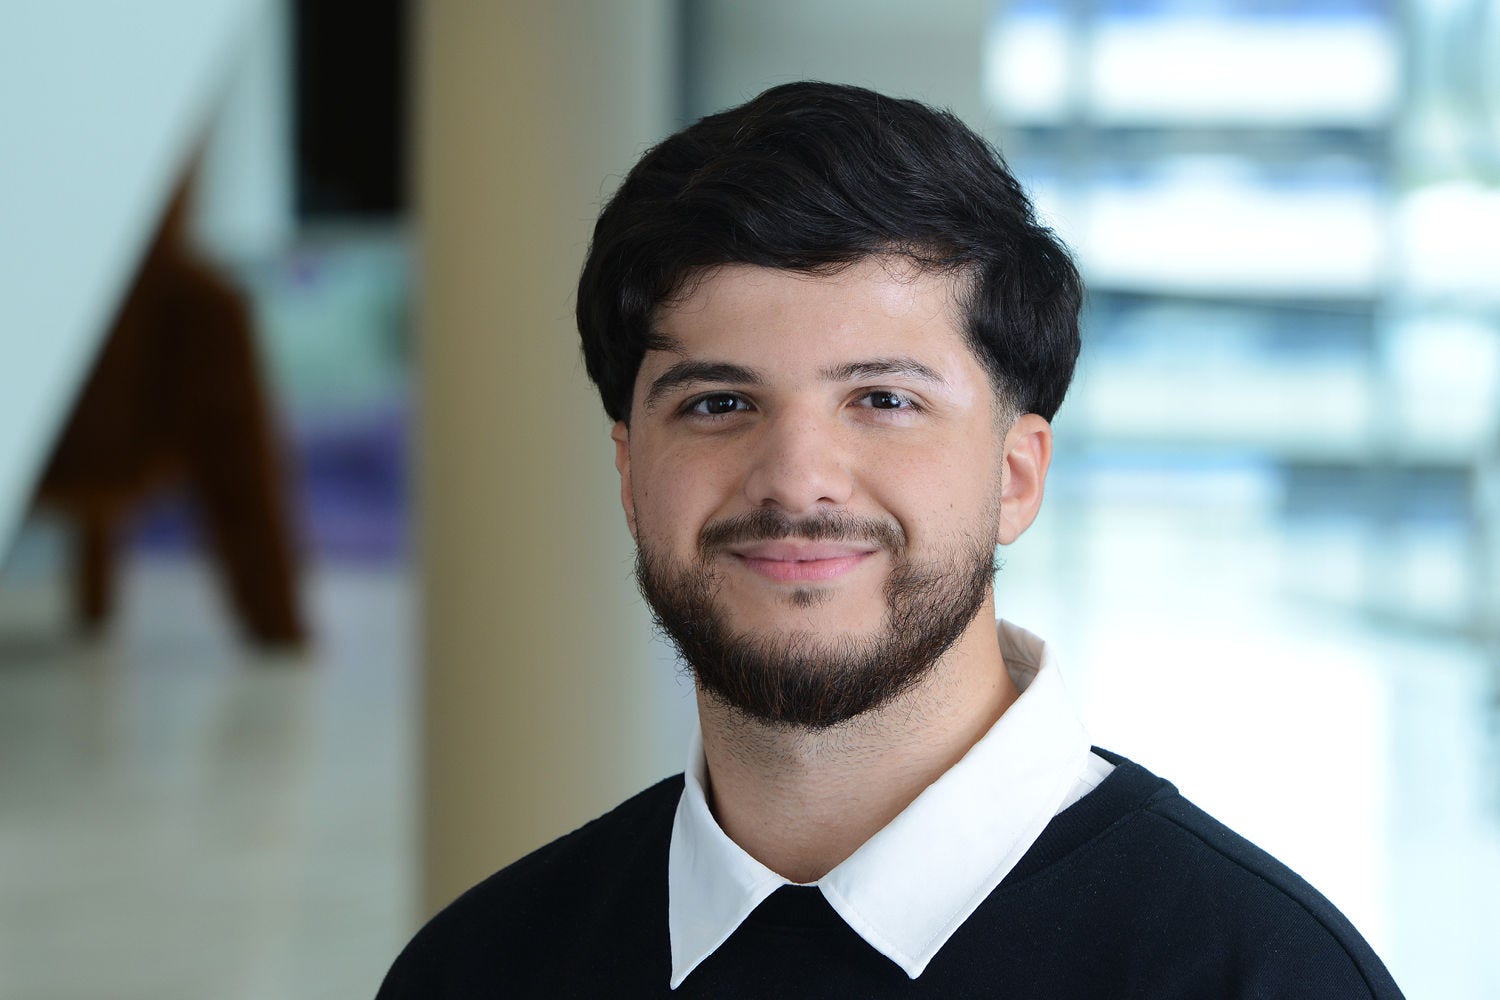
      Amir Oulad Haj Amar, Advisor

      Amir Oulad Haj Amar, Advisor, Enterprise Risk Services

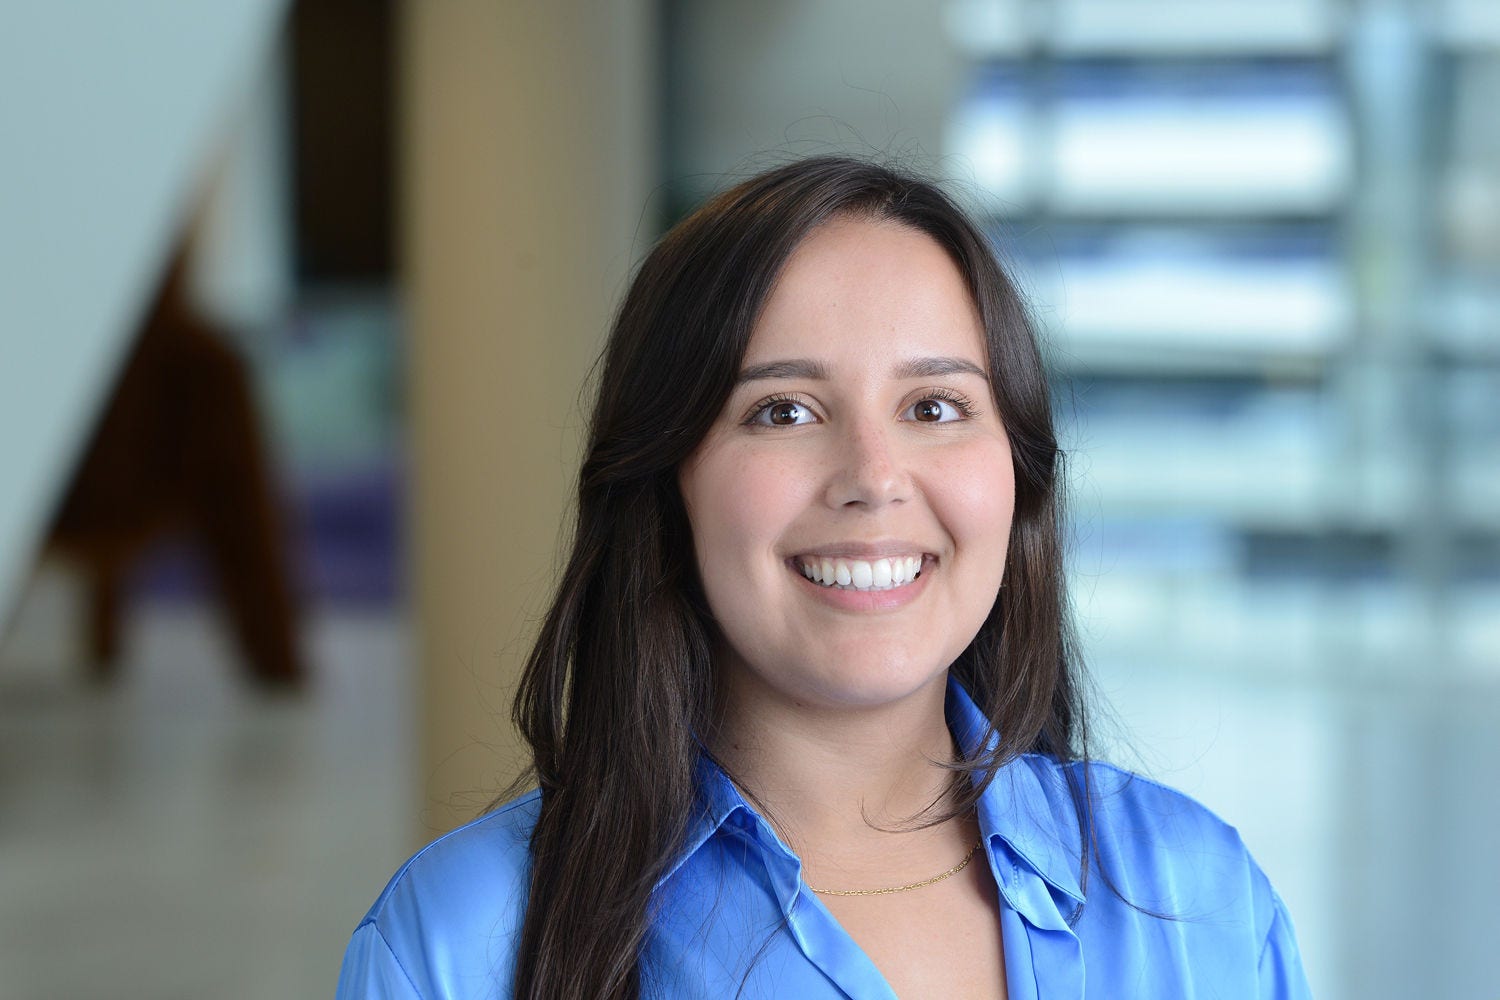
      Safae Assila, Jr Advisor

      Safae Assila, Jr. Advisor, Enterprise Risk Services

      You mentioned important and essential entities. What is the difference between the two?

      Safae: Essential entities are the ones whose disruption would have a major impact on society or the economy, like energy providers and banks. If banking transfers stop, or electricity goes down, the whole economy is affected. Important entities also provide key services, but their disruption isn’t immediately critical. 

      What are the main challenges on NIS2 projects?

      Amir: For me, the biggest challenge is awareness. Many organizations, especially outside of IT, are still unclear about what NIS2 requires, how it affects them, and why urgency is needed. Cybersecurity teams may understand the directive, but HR, procurement, and operational teams often don't realize they now have direct responsibilities.

      Safae: Another major challenge is change management. New policies and procedures are needed across governance, IT, OT, and supply chains. Some stakeholders embrace the change, while others resist, especially when the new requirements impact well‑established processes.

      What is your most memorable NIS2 project so far? What about your dream NIS2 project?

      Amir: For me, it was drafting policies and procedures for a large port organization. I discovered how companies operate differently from one another and understood the importance of tailoring governance documents to the client’s context. It was interesting to understand how they work and apply NIS2 in their context.

      As for my dream project, I would choose working on a hospital. Cybersecurity in healthcare is directly linked to patient safety, making the work highly meaningful.

      Safae: The most memorable NIS2 project for me was an oil and energy company project. The biggest challenge was applying NIS2 to OT environments. OT is really different from IT, and I learned so much about how industrial operations work. It was eye‑opening.

      Regarding my dream NIS2 project, I’d love to do a full transformation journey: gap assessment, roadmap, and implementation, ideally in the aviation sector.

      How did you end up at KPMG?

      Safae: I initially chose KPMG for my internship because of its strong reputation, but I quickly realized it was a place I genuinely enjoyed. My thesis on well‑being in consulting also reinforced how much people matter in this environment, and it’s really the supportive culture and learning opportunities that convinced me to stay. I also took part in, and won, the KPMG Business Case Competition, which became my first real introduction to cybersecurity.

      Amir: I originally studied finance and audit, but during my master’s I started to choose more tech courses. I wrote my thesis on NIS2 and did an internship in cybersecurity. However, the internship was very high‑level. I wanted a more practical, hands‑on experience. KPMG gave me that. And similar to Safae, I also participated in the KPMG Business Case Competition.

      Why should people join KPMG?

      Amir: You get to try a bit of everything - IT audit, GRC, cyber, certification - and then choose what you like. The team spirit also makes coming to the office very enjoyable.

      Safae: You get to learn so much, so fast. Different companies, different projects, different realities - and the people really matter.


      Risky Business Magazine | March 2026

      KPMG in Belgium's Risky Business Magazine explores the latest developments, challenges, and opportunities in cybersecurity, risk management, technology, and business transformation. In each edition, our experts take a deep dive into a key topic, offering practical insights to help organizations navigate emerging risks and make informed decisions.

      In this edition, we focus on NIS2.

      Browse the full magazine below or explore previous editions in our Cybersecurity insights hub.


      Do you have questions related to NIS2?

      For guidance or further information on NIS2-related topics, feel free to reach out to Benny Bogaerts.

      Benny Bogaerts

      Partner, Technology | Advisory

      KPMG in Belgium


      Digital Risk Management

      KPMG Technology services.
      Technology advisory

      Stay informed

      Be the first to know about top business trends that can drive success for your company.

      stay informed